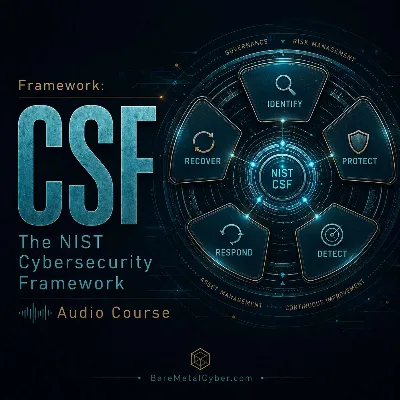
Framework: The NIST Cybersecurity Framework (CSF)
Jason Edwards Visit website › Technology · EN · 114 episodes · latest 2025-10-13
What it is about
Publisher’s own description, taken unchanged from the podcast feed.
© 2026 Jason Edwards
Listen
Available at these services — the RSS feed works in any podcast app.
Latest episodes
-
Dive into a fast, no-fluff overview of what this podcast delivers, who it’s for, and how each episode helps you level up with practical, real-world takeaways. In this trailer, you’ll hear the show’s promise, the format…
-
RC.CO-04 involves sharing public updates on incident recovery using approved channels and messaging, such as breach notifications or preventative steps, to inform affected parties or the broader community. This ensures…
-
RC.CO-03 ensures recovery activities and progress are shared with designated stakeholders—like leadership and suppliers—consistent with response plans and agreements. This includes regular updates on restoration status,…
-
RC.RP-06 declares the end of recovery once predefined criteria are met, finalizing the process with a comprehensive after-action report detailing the incident, actions, and lessons learned. This formal closure ensures…
-
RC.RP-05 verifies the integrity of restored assets—checking for lingering threats or root causes—before returning systems to production, confirming normal operations. This involves testing restoration adequacy to ensure…
-
RC.RP-04 considers critical mission functions and cybersecurity risks to define post-incident operational norms, using impact records to prioritize restoration order. This involves collaboration with system owners to…
-
RC.RP-03 ensures backups and restoration assets are checked for integrity—free of compromise or corruption—before use in recovery efforts. This verification prevents reintroducing threats or using unreliable data,…
-
RC.RP-02 involves selecting, scoping, and prioritizing recovery actions based on incident response plan criteria and available resources, adapting as needs shift. This ensures efforts focus on critical systems first,…
-
RC.RP-01 initiates the recovery phase of the incident response plan once triggered, ensuring all responsible parties are aware of their roles and required authorizations. This begins during or after containment,…
-
RS.MI-02 ensures incidents are fully eradicated, removing threats like malware or unauthorized access through automated system features or manual responder actions. This can involve third-party support, such as MSSPs,…
Episode details from the publisher’s feed. Playback happens at the publisher.
Publisher details
- Oldest episode in feed
- 02/2025 · over a year
- Typical length
- 20 min
- Format
- Serial Meant to be heard in order
- Keywords
- cybersecurity, nist, technology, educational, certification, hacking, blue team, red team
Framework: The NIST Cybersecurity Framework (CSF) in the rankings
For podcasters
Is this podcast yours? Verify it — afterwards you can correct details, get the widget for your website, and we let you know when your podcast is nominated or wins.
Without an account you can use an email address on your show’s own domain — we create the account along the way. The other methods need a login.
Similar podcasts
 Certified: The CompTIA Security+ V8 / SY0-801 Audio Course
Audio course on cybersecurity fundamentals for the CompTIA Security+ exam
Jason Edwards
 Machine Gods
News and analysis of artificial intelligence development and impact
NPR
 "The Cognitive Revolution"
Biweekly interviews with AI builders on emerging technology and its impacts
Erik Torenberg, Nathan Labenz
 3PL Live
Interviews with founders and technologists working in freight technology
Jeremy Thone
 80,000 Hours Podcast
In-depth conversations on artificial intelligence and its global impact
The 80,000 Hours team
 9to5Mac Daily
Daily recap of Apple news and product updates
9to5Mac